Finding CVEs in WordPress: CVE-2026-39531, SQL injection in WP Directory Kit
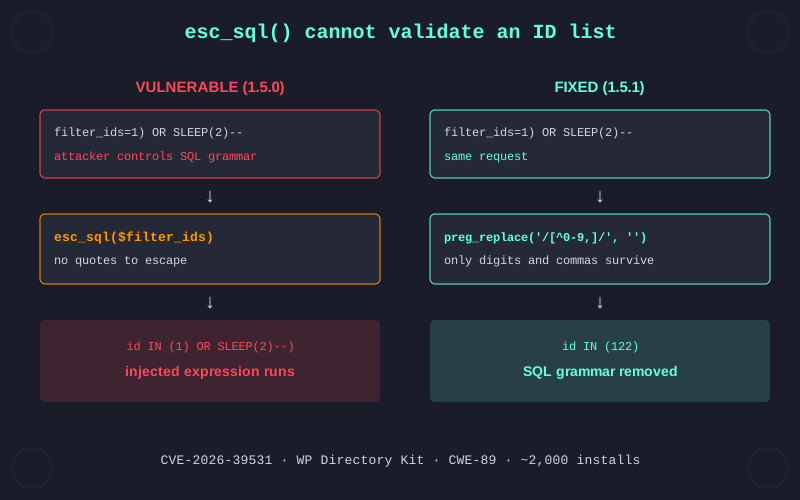
WP Directory Kit passed filter_ids through esc_sql() and inserted it unquoted into an IN clause. Quotes were never needed, so the escaping solved the wrong problem. How the bug worked across three sinks in two methods, why the public nonce did not make it authenticated, and how to find the same pattern.
Read more →